 Design
 App Development
 Web Engineering
 AI Services
 Cloud
 Staffing
 Startups
 Health / Fitness
 Education
 Social
 Nonprofit
 Fintech
 Construction
 Logistics
 Government
 Travel/Hospitality
 HR Software
 About Simpalm
 Our News
 Client Testimonials
 Careers
 Our Blog
 Awards
 Resources
 Information
Key Takeaways
- Treat the proposed 2025 HIPAA Security Rule as today’s security baseline. Controls like MFA, encryption, and stronger risk management are already expected in practice.
- HIPAA penalties are higher than ever. In 2026, civil fines can reach $2.19 million per violation category per year.
- Risk analysis is OCR’s (Office for Civil Rights) biggest enforcement focus. Most recent HIPAA settlements stem from missing or incomplete security risk assessments.
- Business associates are directly accountable. Healthcare software vendors and app developers handling PHI face the same enforcement risks as covered entities.
- Build compliance from day one. Designing for HIPAA early is significantly cheaper and more effective than retrofitting security after launch.
________________________________________________________________________________________
Building a healthcare app is not primarily a design and engineering exercise. It is a compliance exercise first, and a product exercise second, because a single missed access control or an unencrypted backup can turn a promising product into a federal investigation. The Health Insurance Portability and Accountability Act has governed how healthcare data is protected since 1996, and while the core law has stayed largely intact, the way OCR (Office for Civil Rights) enforces it, and the technical bar for what counts as reasonable security have shifted meaningfully in the last two years.
If your product roadmap includes anything that touches a patient’s health information, whether that is a telehealth platform, a patient portal, a remote monitoring app, a mental health app, or a scheduling tool for a clinic, it needs to strictly adhere to HIPAA regulations. This guide walks through what HIPAA actually requires of an app in 2026 and how to build that compliance into your architecture rather than bolting it on after the fact.
What is HIPAA, and Who Does it Actually Apply To?
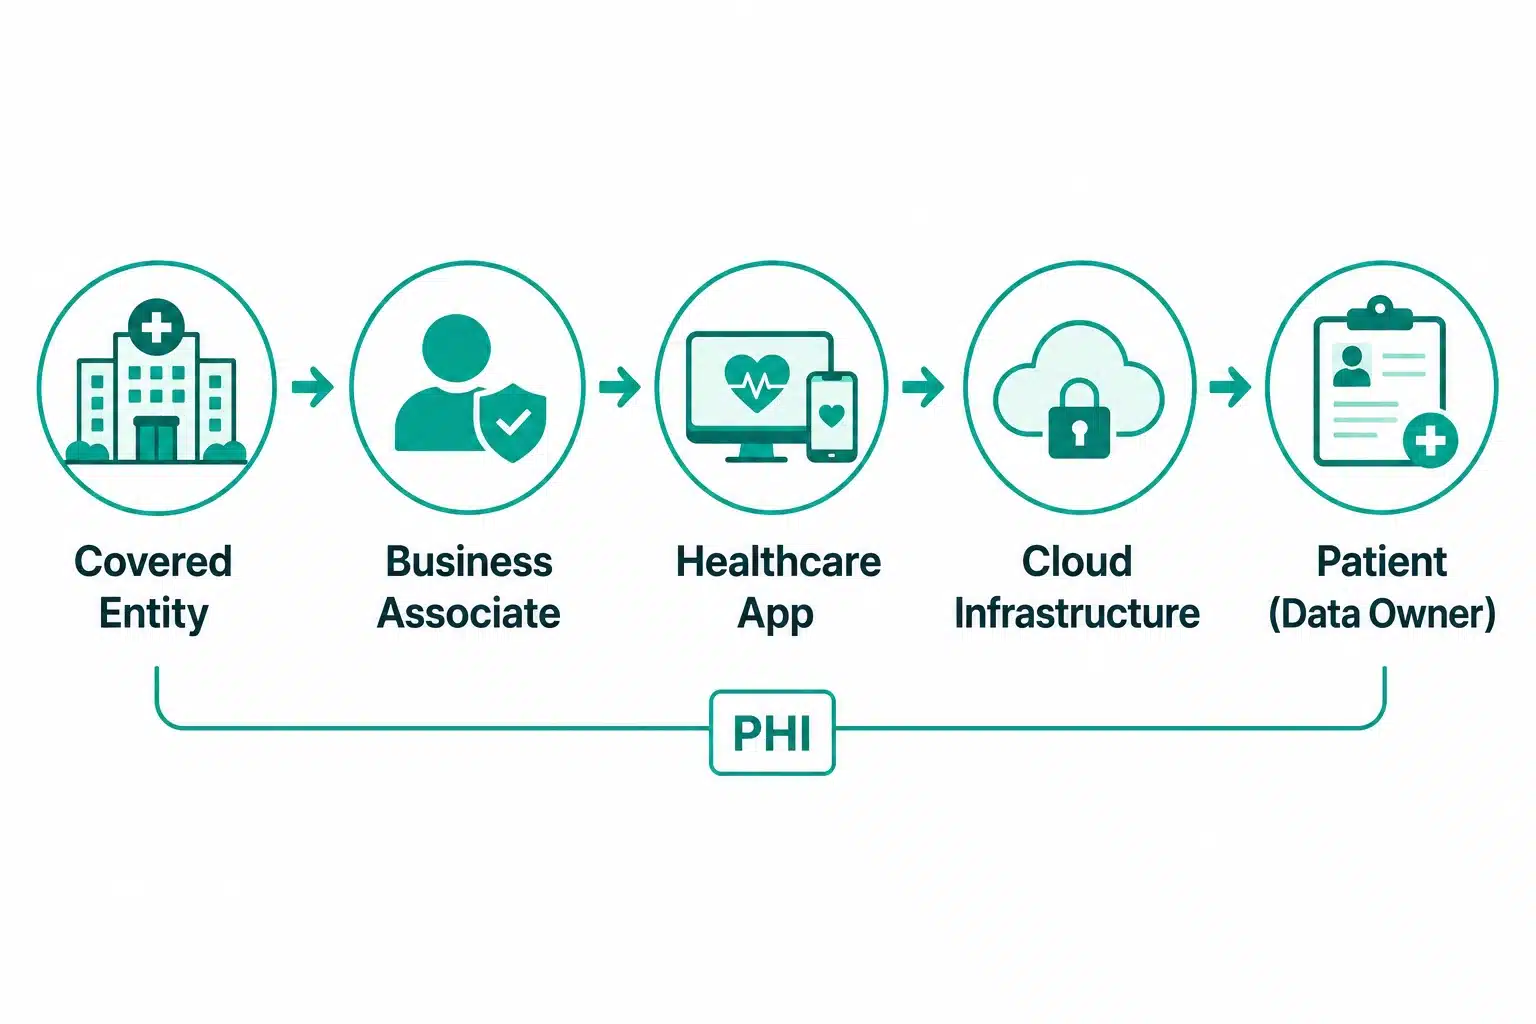
HIPAA applies to two categories of organizations: covered entities and business associates. A covered entity is a health plan, healthcare clearinghouse, or healthcare provider that transmits health information electronically in connection with a covered transaction. A business associate is any person or company that creates, receives, maintains, or transmits protected health information on behalf of a covered entity, which is exactly where most healthcare app developers and their products fall.
This is the detail founders most often misjudge. You do not need to be a hospital or an insurer to fall under HIPAA. If your app processes, stores, or transmits protected health information for a healthcare provider, even indirectly through an API integration or a hosting arrangement, you are almost certainly a business associate and are directly liable under the law, not just contractually liable to your client.
Under HIPAA, covered entities and business associates must:
- Post a Notice of Privacy Practices that describes how protected health information is used and disclosed.
- Obtain a signed Business Associate Agreement with every vendor that touches PHI on their behalf, and execute one as a business associate with every covered entity client before any PHI enters the system.
- Implement administrative, physical, and technical safeguards under the Security Rule to protect electronic protected health information.
- Give patients the right to access, request corrections to, and receive an accounting of disclosures of their health information.
- Report breaches affecting 500 or more individuals to HHS and the media within 60 days, and notify affected individuals without unreasonable delay.
Civil penalties are no longer a rounding error for a growing app. As of the inflation adjustment that took effect January 28, 2026, penalties range from $145 to $73,011 per violation depending on culpability tier, with a maximum annual cap of $2,190,294 for willful neglect that is not corrected. OCR counts each affected record or each distinct violation type separately in many cases, which is how settlements climb into seven figures even for a single incident.
Also Read: Chronic Care Management Software Guide for 2026
What’s Changing: The Proposed 2026 HIPAA Security Rule Update
A significant share of HIPAA content circulating today still reflects the 2013 version of the Security Rule. HHS published a Notice of Proposed Rulemaking in January 2025 proposing the first substantial overhaul of the Security Rule in over a decade, and while it has not been finalized, it signals clearly where OCR’s enforcement expectations are already heading.
| Area | Current Security Rule (2013) | Proposed 2026 Update |
| Addressable specifications | Implementation specifications are split into “required” and “addressable,” with addressable items open to a documented alternative or a reasonable justification for non-implementation | Eliminates the “addressable” category entirely; nearly every implementation specification becomes mandatory with only narrow, documented exceptions |
| Encryption | Encryption of ePHI at rest and in transit is addressable, meaning organizations can justify not implementing it | Encryption becomes a required, non-negotiable control for ePHI at rest and in transit |
| Authentication | No explicit multi-factor authentication requirement | Multi-factor authentication required for all access to systems containing ePHI |
| Network architecture | No explicit segmentation requirement | Requires documented network segmentation to limit lateral movement in the event of a breach |
| Incident response | Breach notification required within 60 days | Introduces a much shorter internal reporting expectation, with proposals for 24 to 72 hour timelines for notifying affected business partners of a security incident |
| Risk analysis | Required but loosely defined in practice | Tightened into a more prescriptive, evidence-backed process with a documented technology asset inventory across every ePHI-touching system |
The practical effect for development teams is significant regardless of whether the rule finalizes as written. If your app stores ePHI without encryption at rest because encryption felt optional, that gap is already a known deficiency category in OCR’s current risk analysis enforcement initiative. Building to the proposed standard now, rather than waiting for a final rule, means your architecture is compliant today and largely future-proofed against whatever version ultimately publishes. You can review the full text of the proposed rule directly in the Federal Register if your compliance team wants the source document.
What Counts as Protected Health Information (PHI)
Before your team can design a compliant data flow, everyone needs a shared, current understanding of what counts as protected health information. HIPAA defines 18 identifiers that, combined with health information, turn ordinary data into PHI, and several of them are easy to overlook during a technical spec review.
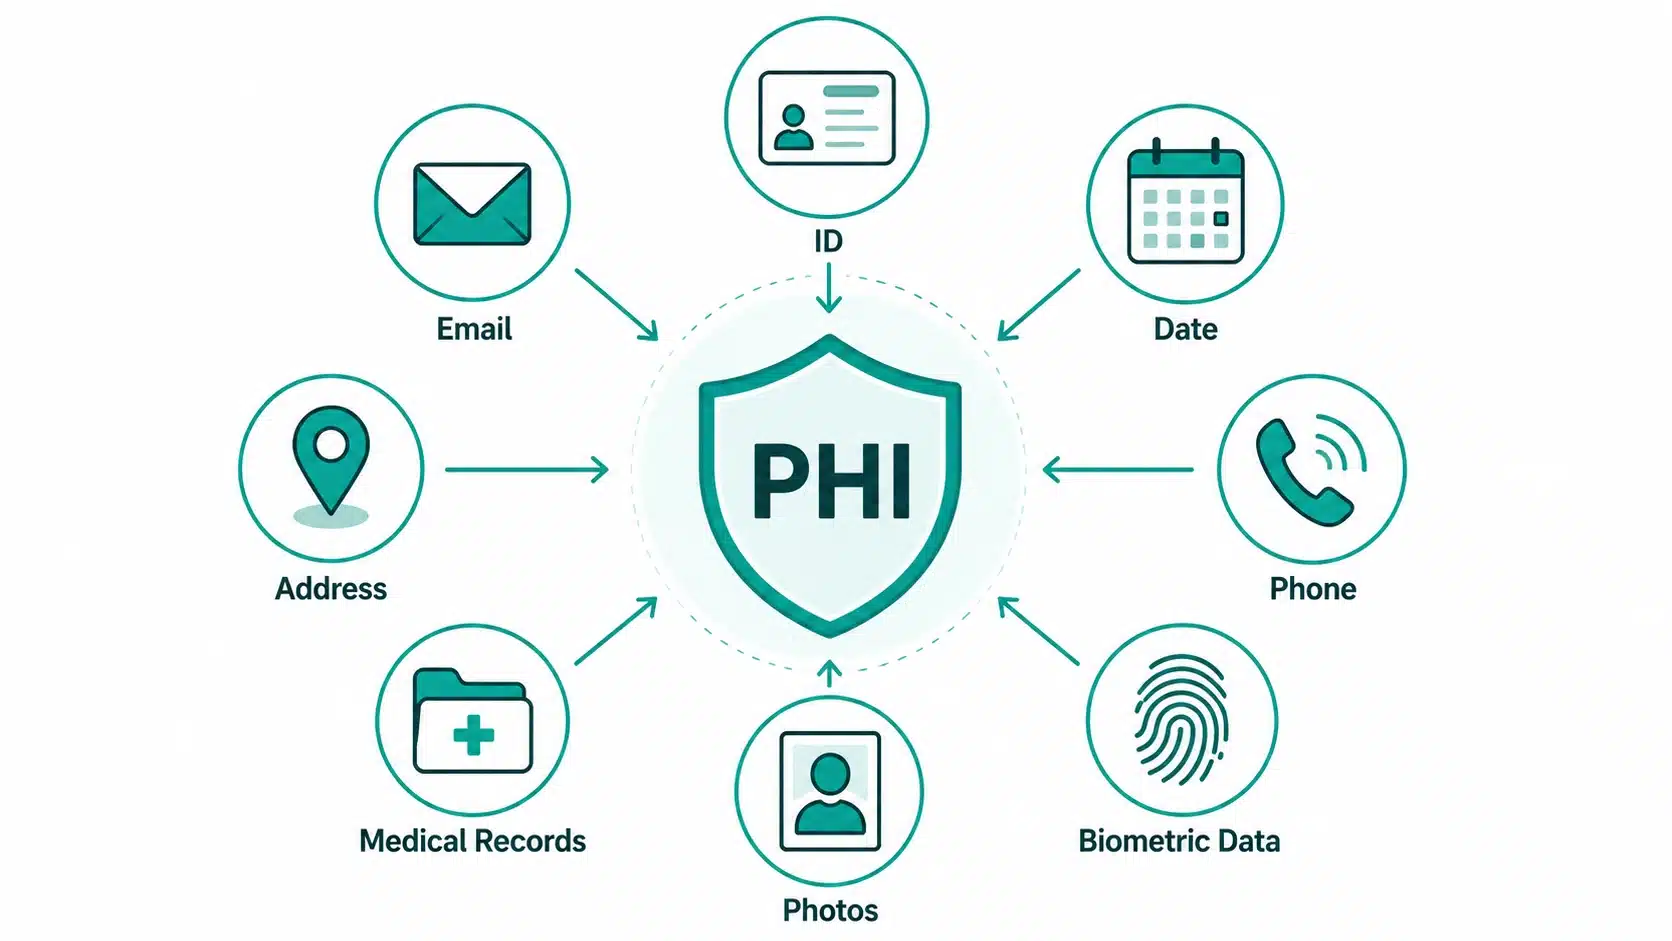
Here are the key data categories that count as PHI:
| Category | Examples | Commonly Missed By Dev Teams |
| Direct identifiers | Name, address, phone number, email, Social Security number | Rarely missed |
| Dates | Birth date, admission and discharge dates, date of death, any date more specific than year tied to an individual | Frequently missed in analytics dashboards that log timestamps by default |
| Online and device identifiers | IP addresses, device IDs, URLs, biometric identifiers | Often missed when using default analytics or crash-reporting SDKs |
| Medical record and account numbers | Health plan beneficiary numbers, medical record numbers, account numbers | Rarely missed in core clinical data, but often missed in support ticket systems |
| Images | Full-face photographs and comparable images | Frequently missed in telehealth apps with video or photo-based intake features |
| Free-text and derived data | Clinical notes, chat transcripts, AI-generated summaries containing any of the above | Often missed when free-text fields are treated as unstructured, non-PHI data |
| Any other unique identifying number or code | Device serial numbers, license plate numbers, any code that could re-identify a person | Frequently missed in logging and debugging tools that capture more context than intended |
A useful working rule for engineering teams: if a data point, combined with any health-related context, could reasonably identify a specific patient, treat it as PHI until your compliance team confirms otherwise. This applies just as much to a debug log or an analytics event as it does to a clinical record.
Step-by-Step: Building HIPAA Compliance Into Your App
Knowing the legal requirements does not tell your engineering team how to actually build the product. Compliance has to live in your architecture, not just your privacy policy and your Business Associate Agreements.
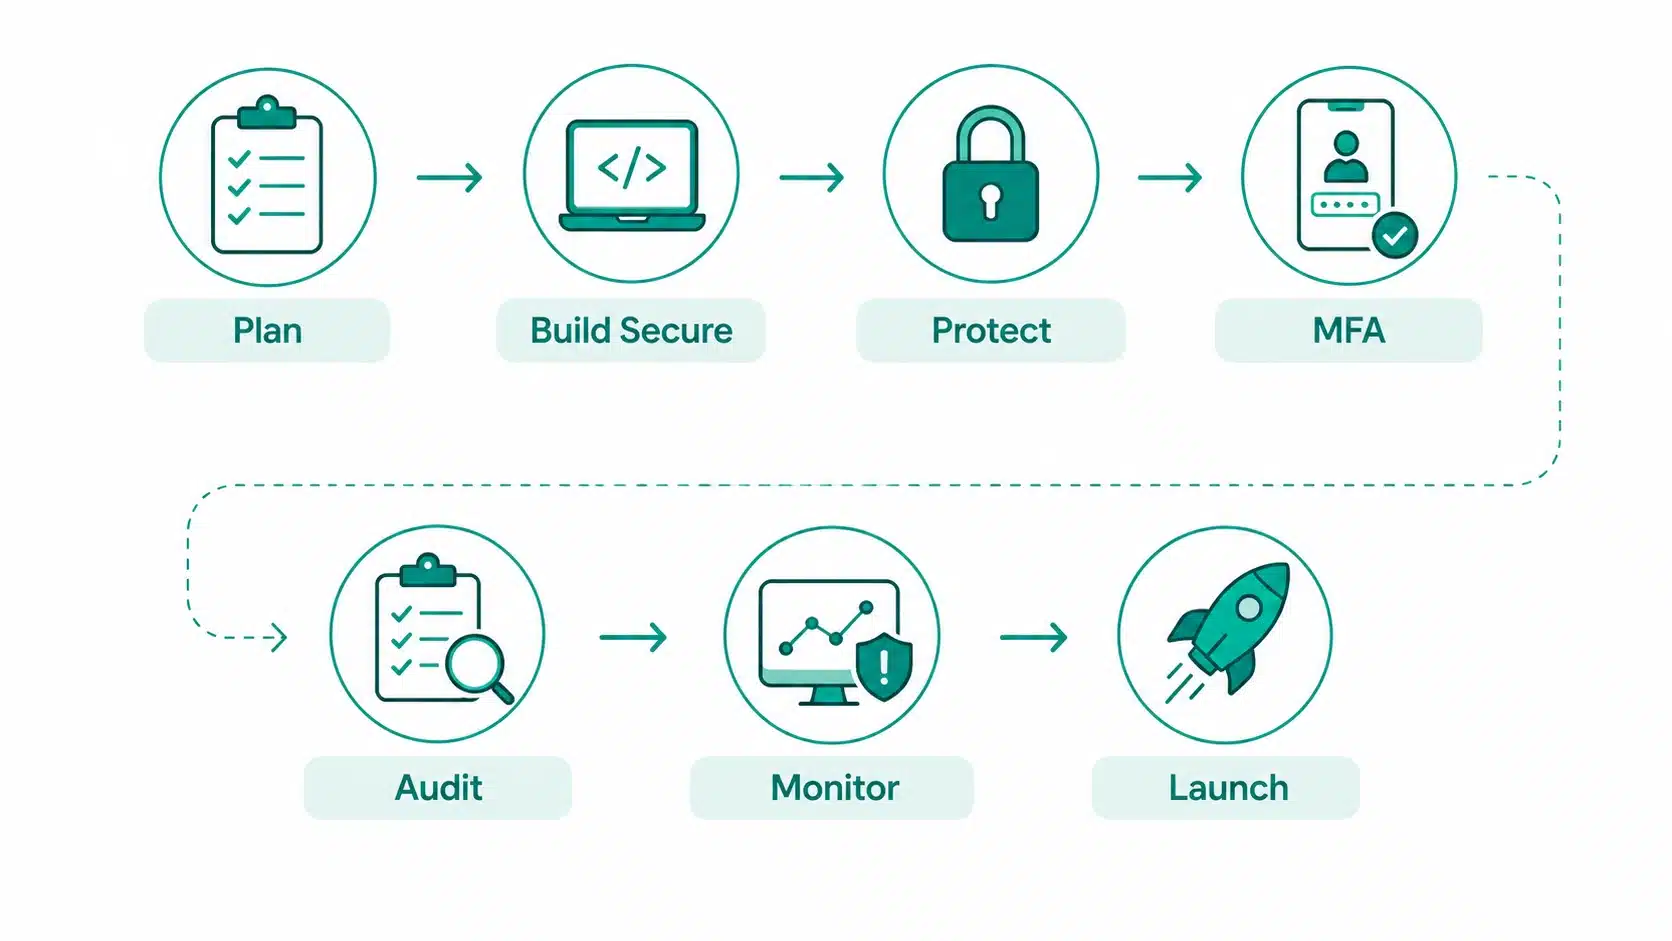
Here’s step by step process to build HIPAA right into the app’s architecture:
Step 1: Confirm Your Role and Lock Down Business Associate Agreements Before Any PHI Moves
Before a single line of code touches real patient data, confirm whether your company is a covered entity, a business associate, or a subcontractor to a business associate. Then make sure a signed Business Associate Agreement exists with every party in that chain, including your cloud hosting provider, your analytics vendor, your email service, and any AI or third-party API you plan to route PHI through. A missing BAA with even one vendor is one of the fastest ways to turn a routine product decision into a compliance gap.
Step 2: Architect Role-Based Access Control and Audit Logging From the Start
The Security Rule requires the minimum necessary standard, meaning users should only be able to access the PHI required for their specific role. This needs to be a database and API-level decision, not a UI-level one. Build role-based access control into your permissions schema from the first sprint, and log every access, view, and modification of PHI with enough detail to reconstruct who touched what data and when. Retrofitting audit logging after launch usually means rebuilding large parts of your data access layer.
Step 3: Treat Encryption as Mandatory, Not Optional
Even under the current rule, where encryption is technically addressable, OCR consistently cites missing encryption as a Security Rule deficiency in its enforcement actions. Encrypt ePHI at rest using strong, current standards, and encrypt it in transit using TLS for every connection, including internal service-to-service calls, not just the client-facing API. Under the proposed rule, this becomes a required control with no addressable alternative, so building it in now avoids a costly retrofit later.
Step 4: Implement Multi-Factor Authentication and Strong Session Management
MFA is already a best practice OCR expects to see during a risk analysis review, and it is a near-certain requirement under the finalized Security Rule. Build MFA into your authentication flow for every user type that can access ePHI, including internal admin and support tooling, which is a surface area teams frequently forget to cover. Pair this with short, enforced session timeouts and automatic logoff for idle sessions.
Step 5: Design for Data Minimization and Purpose-Limited Collection
Before your team writes a data model, ask whether each field is actually necessary to deliver the feature. A medication reminder app needs a medication name and a schedule. It does not need a full diagnosis history unless a specific feature requires it. Every additional PHI field you collect is additional compliance surface area, additional breach exposure, and additional audit scope.
Step 6: Build Breach Notification and Incident Response Into the Product, Not Just the Policy
HIPAA requires notification of affected individuals and HHS within specific timeframes after a breach is discovered, and the proposed rule pushes internal reporting timelines even tighter. Your engineering team needs monitoring in place that can actually detect anomalous access to ePHI, not just a written incident response plan that nobody has tested. Build automated alerting for unusual access patterns, failed authentication spikes, and bulk data exports, since these are the events that most often precede a reportable breach.
Step 7: Conduct a Documented Risk Analysis Before Launch, and Repeat It Continuously
A HIPAA risk analysis is not a one-time checkbox before your first covered entity client signs a contract. It needs to be an accurate, thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of your ePHI, documented in writing, and revisited whenever you add a new feature, vendor, or data flow. This single document is the difference, in nearly every 2025 OCR settlement, between an organization that could demonstrate reasonable diligence and one that could not.
Also Read: Step by Step Process for How to Develop a Healthcare App
App Store and Google Play Requirements for HIPAA Apps in 2026
Both major platforms layer their own review expectations on top of HIPAA, and missing them can delay a launch even when your underlying compliance posture is solid.
Apple requires health apps to clearly disclose what health data is collected, how it is used, and whether it is shared with third parties, and apps that integrate with HealthKit face additional restrictions on using that data for advertising or selling it to data brokers. Apple’s review process for health-adjacent apps has grown more detailed in recent cycles, with reviewers specifically checking for a clear, accessible privacy policy and appropriate consent flows before granting access to sensitive health permissions.
Google Play requires apps handling health data to complete its Data Safety disclosure accurately, describing exactly what health information is collected and how it is secured. Google has also increased scrutiny on apps that request broad permissions, such as camera, microphone, or location access, without a clear feature-level justification tied to the app’s core health functionality.
Build extra review time into your launch timeline for both platforms rather than assuming a fast turnaround, particularly if your app touches sensitive categories like mental health or reproductive health data.
What Non-Compliance Actually Costs: 2025’s Enforcement Record
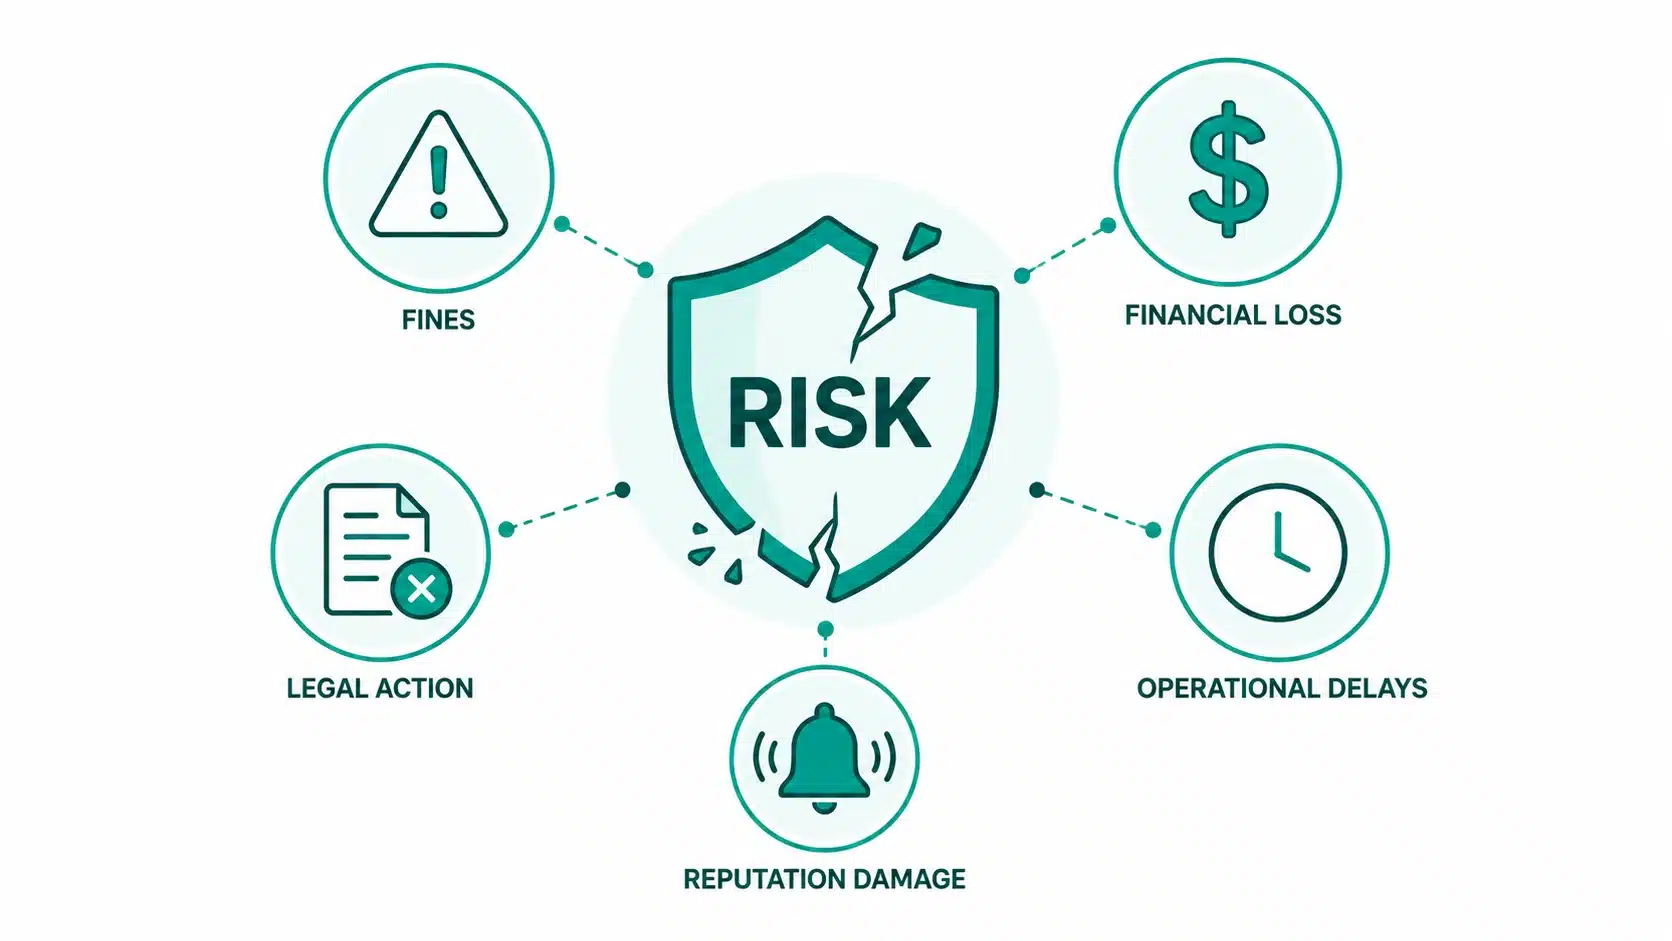
HIPAA enforcement stopped feeling theoretical for a lot of founders once the 2025 numbers came in. OCR closed 21 settlements and civil monetary penalties in 2025, the second-highest annual total on record, collecting a significant sum from organizations of every size.
| Organization | Settlement | What Went Wrong |
| Solara Medical Supplies (subsidiary of AdaptHealth) | $3 million | A 2019 phishing attack compromised multiple employee email accounts, exposing the health data of over 114,000 individuals |
| MMG Fusion, LLC (business associate) | $10,000 plus a three-year corrective action plan | Impermissibly disclosed PHI of approximately 15 million individuals, failed to conduct a risk analysis, and failed to timely notify affected covered entities of the breach |
| BayCare Health System | $800,000 | Failed to revoke former employees’ access credentials and lacked adequate policies to prevent improper credential use, discovered after unauthorized record access |
| Warby Parker | Civil monetary penalty | Cited for inadequate risk analysis, insufficient security measures, and no procedures to review system activity logs |
| Concentra, Inc. | $112,500 | Failed to provide a patient timely access to their own health records despite repeated requests, resolved under OCR’s Right of Access enforcement initiative |
What connects nearly every one of these cases is not malicious intent. It is a documented failure to complete or maintain a thorough risk analysis, a gap in access control hygiene, or a slow response to a patient’s access request. Each of those is a fixable, architectural problem when addressed during development, and a far more expensive one when discovered after a breach or a complaint.
How Much Does it Cost to Build a HIPAA Compliant App?
Compliance cost depends heavily on whether you build it in from day one or retrofit it after the fact. Retrofitting is consistently the more expensive path because access control, encryption, and audit logging touch your database schema, your API design, and your infrastructure all at once, not just a single feature.
| App Tier | What You Get | Estimated Cost | Timeline |
| Basic MVP | Core features, encrypted data storage, role-based access, signed BAAs with vendors, basic audit logging | $40,000 – $75,000 | 3–5 months |
| Mid-Tier | Full feature set, MFA, detailed audit trails, third-party vendor risk assessment, documented risk analysis, breach detection monitoring | $80,000 – $180,000 | 5–9 months |
| Enterprise-Grade Platform | Full compliance program, SOC 2 or HITRUST readiness, multi-region hosting, advanced anomaly detection, dedicated compliance and security engineering | $200,000+ | 9–18 months |
What Drives Cost Up
HIPAA compliance adds cost because security must be built into every layer of the application, not added later. Legal reviews, Business Associate Agreements (BAAs), and security risk assessments require ongoing updates as your app evolves. Engineering effort also increases with encryption, role-based access, MFA, audit logging, and continuous monitoring.
Every third-party vendor must be vetted for HIPAA eligibility and BAA support, while penetration testing and compliance audits add further expense. Overall, a HIPAA-compliant app typically costs 20–30% more than a similar non-compliant app due to the additional security, documentation, testing, and compliance requirements.
Ongoing Cost
Legal and compliance review is not a one-time cost. Your Business Associate Agreements, risk analysis, and breach notification procedures should be reviewed by counsel before launch and again any time you add a feature, vendor, or data flow that touches ePHI.
Vendor and infrastructure vetting takes real engineering time. Confirming that every third-party service, from your cloud host to your customer support tool, offers a signable BAA and a HIPAA-compliant configuration often adds weeks to a build that founders rarely budget for upfront.
Audit-ready logging and monitoring infrastructure is a real engineering investment, not a checkbox. Building the kind of detailed, queryable access logs that can actually reconstruct an incident timeline takes more effort than basic application logging.
Where You Can Optimize Without Cutting Corners
Choose cloud infrastructure providers that already offer HIPAA-eligible services and a standard BAA rather than negotiating custom data handling agreements from scratch. Use established authentication and identity providers that support MFA out of the box instead of building custom authentication infrastructure. Start with a single, well-scoped feature set before expanding into more complex integrations, so your compliance architecture gets validated once before you multiply your surface area.
HIPAA Versus Other Health Privacy Laws

If your app’s distribution plan includes markets outside the United States, or if your data touches particularly sensitive categories, HIPAA is the floor, not the whole picture.
| Law | Jurisdiction | Scope | Key Difference From HIPAA |
| HIPAA | United States | Covered entities and business associates handling PHI | Federal law, OCR-enforced, focused on covered transactions and specific identifier categories |
| 42 CFR Part 2 | United States | Substance use disorder treatment records | Stricter consent requirements than HIPAA for a narrower category of especially sensitive records, now enforced by OCR alongside HIPAA |
| GDPR | European Union | Any organization processing EU residents’ personal data, including health data | Broader in scope, treats health data as a special category requiring explicit consent, and applies regardless of whether an organization is a “covered entity” |
| State health privacy laws (e.g., Washington My Health My Data Act, California CMIA) | Individual US states | Health-adjacent data not always covered by HIPAA, such as data from consumer wellness apps | Often apply to apps and data types HIPAA does not reach, including many direct-to-consumer health and wellness apps that fall outside HIPAA’s covered entity definition |
Building for HIPAA compliance first and expanding into other jurisdictions deliberately is almost always more efficient than trying to satisfy every regime simultaneously from day one. This is especially relevant for consumer-facing wellness and health apps that assume HIPAA does not apply to them, since state-level laws like Washington’s My Health My Data Act have started closing that gap.
Common Mistakes That Trigger OCR Scrutiny
A handful of patterns show up again and again in HIPAA enforcement actions and post-incident reviews.
Skipping or superficially documenting the risk analysis is the single most common finding behind 2025’s enforcement actions, and it is entirely within a development team’s control to get right. Close behind it is failing to execute a Business Associate Agreement with every vendor that touches PHI, which is exactly what turned a routine SDK integration into liability in several recent cases.
On the access control side, the most common mistake is failing to revoke system access promptly when an employee or contractor leaves, which is precisely what triggered the BayCare settlement. A close second is treating encryption as optional because the current rule labels it addressable, a decision that consistently draws OCR scrutiny even before the proposed rule makes it mandatory outright.
On the product side, the most common mistake is building a patient-facing access or export feature without a clear internal process for verifying identity and responding within HIPAA’s required timeframe, which is what drives the steady stream of Right of Access settlements OCR continues to announce.
How Simpalm Approaches HIPAA Compliant Development?
Building for healthcare data is not a feature you add near launch. It has to shape your data model, your vendor selection, your access control architecture, and your QA process from the very first sprint. At Simpalm, HIPAA compliance planning happens during discovery, alongside feature scoping, not after the build is already underway.
If you are building a secured HIPAA compliant healthcare app, make sure the team behind it understands both the current Security Rule and the direction OCR’s enforcement is heading, not just the letter of a decade-old regulation. The gap between a privacy policy that reads well and an architecture that actually enforces it is where most HIPAA violations originate, and it is exactly the gap we work to close from the start of every healthcare engagement.
Conclusion
HIPAA compliance is not a static checklist you finish once. The proposed Security Rule update signals where enforcement expectations are already heading, and OCR’s 2025 enforcement record shows the agency is actively pursuing risk analysis failures, access control lapses, and vendor oversight gaps at every organization size, not just large hospital systems. Apps that treat compliance as architecture, not paperwork, are the ones that survive a covered entity’s vendor review and an OCR investigation alike. That means locked-down access controls, signed Business Associate Agreements before any PHI moves, mandatory encryption, and a risk analysis that actually reflects what your system does in production.
Building this in from day one costs far less than retrofitting it after launch, and it earns the kind of trust that gets your app approved by enterprise healthcare clients, trusted by patients, and overlooked by regulators for the right reasons.
Frequently Asked Questions
Q1. Does HIPAA apply to my app if I am not a hospital or insurance company?
Ans. Yes, if your app creates, receives, maintains, or transmits protected health information on behalf of a covered entity, such as a healthcare provider or health plan, you are considered a business associate and are directly liable under HIPAA. This applies even if your product was originally built as a general wellness or productivity tool, once a covered entity client starts routing patient data through it.
Q2. Is the proposed 2026 HIPAA Security Rule update already in effect?
Ans. No. As of mid-2026, the proposed update remains a Notice of Proposed Rulemaking, not final law. HHS targeted a May 2026 final rule, but that date passed without publication, and there is no confirmed new timeline. The current Security Rule, in effect since 2013, remains what OCR actively enforces in the meantime, though many of the proposed controls already reflect what OCR expects during a risk analysis review.
Q3. What is a Business Associate Agreement, and do I really need one with every vendor?
Ans. A Business Associate Agreement is a legal contract that requires a vendor handling PHI on your behalf to protect that data to HIPAA’s standards. You need a signed BAA with any vendor that could plausibly touch PHI, including cloud hosting providers, analytics tools, email services, and any third-party API. A missing BAA with even one vendor in your stack is a Security Rule gap that OCR treats seriously, regardless of whether that vendor ever actually experiences a breach.
Q4. How much does it cost to build a HIPAA compliant app?
Ans. A basic MVP with core compliance features typically costs $40,000 to $75,000 and takes 3 to 5 months. A mid-tier app with MFA, detailed audit trails, and a documented risk analysis runs $80,000 to $180,000 over 5 to 9 months. Enterprise-grade platforms with SOC 2 or HITRUST readiness and advanced monitoring start around $200,000 and can take 9 to 18 months. Building compliance from the start is consistently cheaper than retrofitting it after launch.
Q5. What happens if my app has a data breach involving patient information?
Ans. HIPAA requires notifying affected individuals without unreasonable delay and no later than 60 days after discovery, and breaches affecting 500 or more individuals must also be reported to HHS and, in many cases, the media. The proposed rule would tighten internal reporting timelines further. Beyond notification, OCR typically opens an investigation that examines whether your organization had conducted an adequate risk analysis and implemented reasonable safeguards before the breach occurred, which is often the deciding factor in how the case resolves.
Q6. Do I need encryption if the current HIPAA rule calls it “addressable” rather than “required”?
Ans. Effectively, yes. While the current rule technically allows an organization to document a reasonable alternative or justification for not encrypting ePHI, OCR consistently cites missing encryption as a deficiency in its enforcement actions, and the proposed rule would remove the addressable option entirely. Building encryption in as a mandatory control from the start avoids both current enforcement risk and a future compliance gap.
Q7. Are consumer health and wellness apps covered by HIPAA?
Ans. Not always. If a wellness app is not created, maintained, or used on behalf of a covered entity, it may fall outside HIPAA’s scope entirely, even though it collects sensitive health data. This gap is exactly why several states have passed their own health data privacy laws, such as Washington’s My Health My Data Act, which apply to consumer health apps regardless of whether HIPAA covers them.
Q8. What is the most common reason HIPAA compliant apps get fined?
Ans. Failing to conduct or maintain an accurate, thorough risk analysis is consistently the most cited finding in OCR’s recent enforcement actions, appearing in the majority of 2025’s settlements. Access control failures, such as not revoking a former employee’s credentials, and missing Business Associate Agreements with vendors are the next most common issues, and both are entirely preventable when addressed during the development process rather than after an incident.