 Design
 App Development
 Web Engineering
 AI Services
 Cloud
 Staffing
 Startups
 Health / Fitness
 Education
 Social
 Nonprofit
 Fintech
 Construction
 Logistics
 Government
 Travel/Hospitality
 HR Software
 About Simpalm
 Our News
 Client Testimonials
 Careers
 Our Blog
 Awards
 Resources
 Information
Key Takeaways
- AI agents differ from chatbots in autonomy, not just capability. A chatbot answers; an agent plans, calls tools, and completes multi-step tasks with minimal human input.
- Architecture choice for building AI agents should follow task complexity, not trends. Simple and rule-bound workflows rarely need a full multi-agent system, and forcing one in adds cost without adding value.
- Most successful AI agent deployments combine a pre-built framework with custom integration work for internal systems.
- Governance and monitoring are not optional add-ons. Gartner expects more than 40 percent of agentic AI projects to be canceled by 2027 due to cost overruns, unclear value, or weak oversight, and most of those failures trace back to skipped governance work early in the build.
_________________________________________________________________________________________
Gartner expects task-specific AI agents to be embedded in 40 percent of enterprise applications by the end of 2026, up from less than 5 percent just a year earlier. That is one of the fastest technology adoption curves Gartner has ever tracked, and it is happening at the same time McKinsey’s 2026 State of AI survey found that large enterprises scaling AI agents in at least one business function jumped from 27 percent to 40 percent in a single year.
The gap between those numbers and what most companies actually deliver is significant. Many teams can explain what an AI agent is, but far fewer can answer the practical questions that determine project success: which architecture best fits the use case, what the implementation realistically costs, how to structure development for reliable production deployment, and how to measure whether the agent is delivering meaningful results.
In this article, you will learn how AI agents are structured, what they realistically cost across different complexity levels, and how to plan and build them for reliable production use, so you can scope your project with confidence instead of guesswork.
What Is an AI Agent, and How Is It Different From a Chatbot?
An AI agent is a software system that can interpret a goal, decide on a sequence of steps to reach it, and carry out those steps using external tools, APIs, or data sources, with limited need for a human to direct every action. That last part is the real distinction.
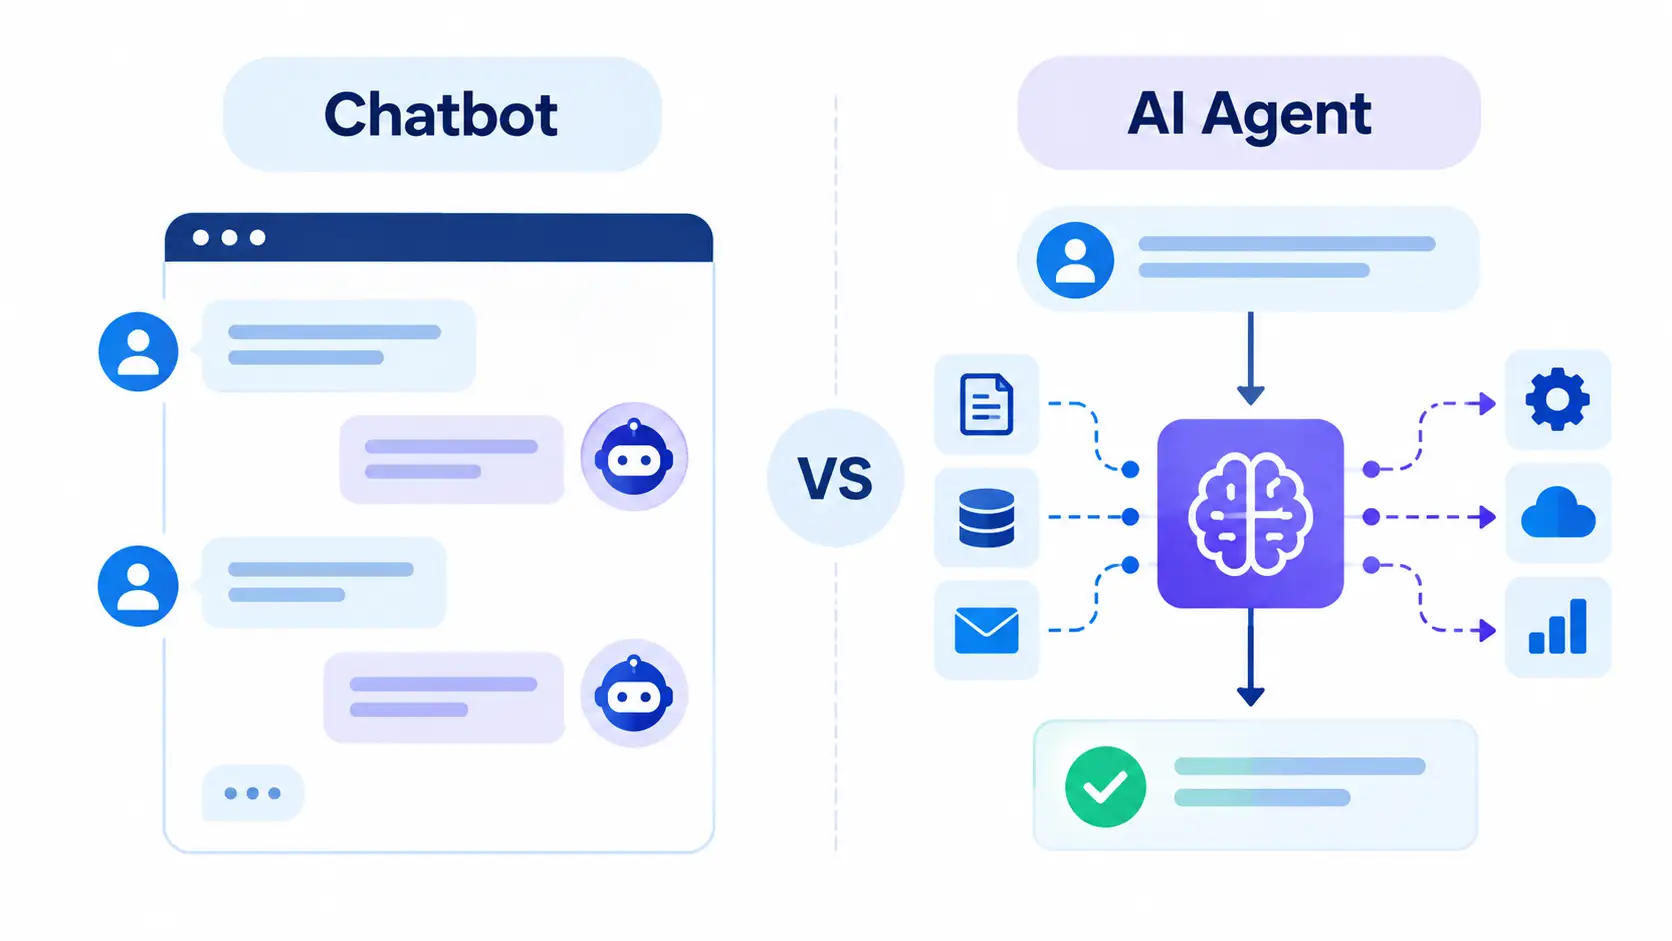
A chatbot answers a question inside a conversation. An agent can take that answer and act on it: updating a record, triggering a workflow, escalating to a human when it hits the edge of its authority.
The clearest way to see the difference is to compare how each one handles the same request. Ask a chatbot “what’s our refund policy?” and it looks up an answer. Tell an agent “process this customer’s refund,” and it has to verify eligibility, check order status, apply the correct policy, execute the transaction, and confirm the outcome, adjusting its approach if any step does not go as expected.
| Feature | Bot | AI Assistant | AI Agent |
| Autonomy | Follows fixed, pre-programmed rules | Responds to prompts, recommends actions | Plans and acts independently toward a goal |
| Task scope | Single trigger, single response | Single-turn help within a session | Multi-step, multi-system task completion |
| Decision-making | None | User makes the final call | Agent decides and executes, escalates on uncertainty |
| Typical example | FAQ auto-responder | In-app support widget | Agent that reconciles an invoice end to end |
This distinction matters more than it might seem, because a huge share of “agent” projects that stall in production were actually scoped as elaborate chatbots. If the system genuinely just answers questions, building agent-level infrastructure around it adds cost without adding value. The rise of AI in app development has made this distinction increasingly important for teams deciding where AI actually belongs in their product.
What are core components of AI Agent Architecture?
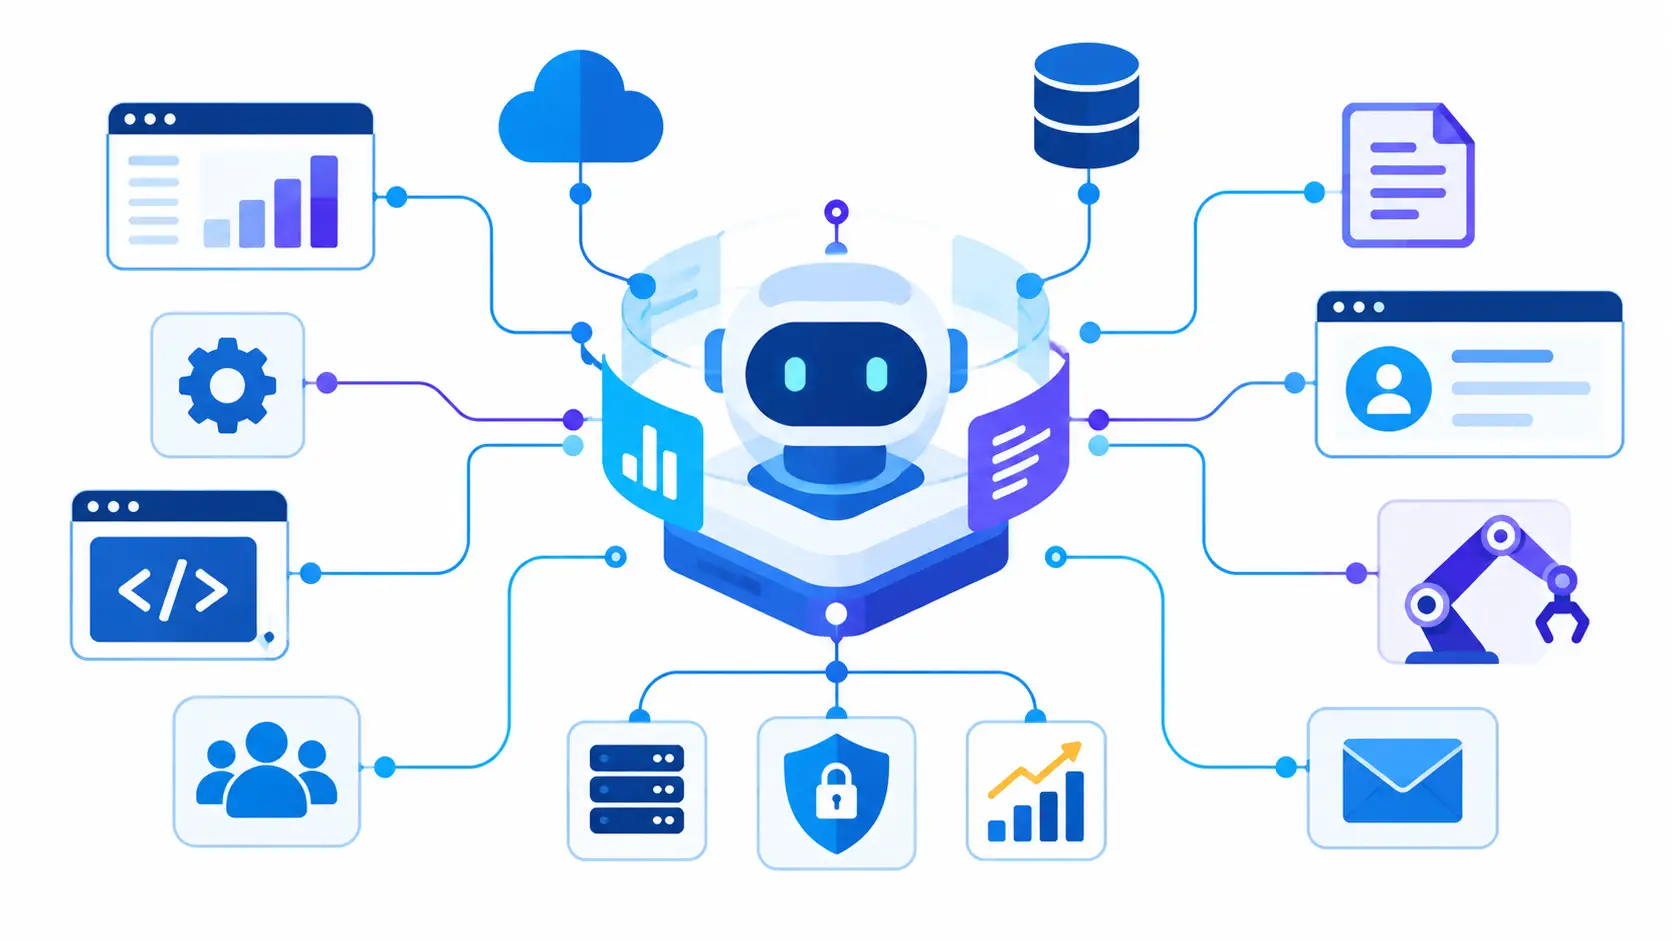
Every functional AI agent, regardless of what it does, is built from the same core components. Understanding them lets you scope a project accurately instead of taking a vendor’s word for what you need.
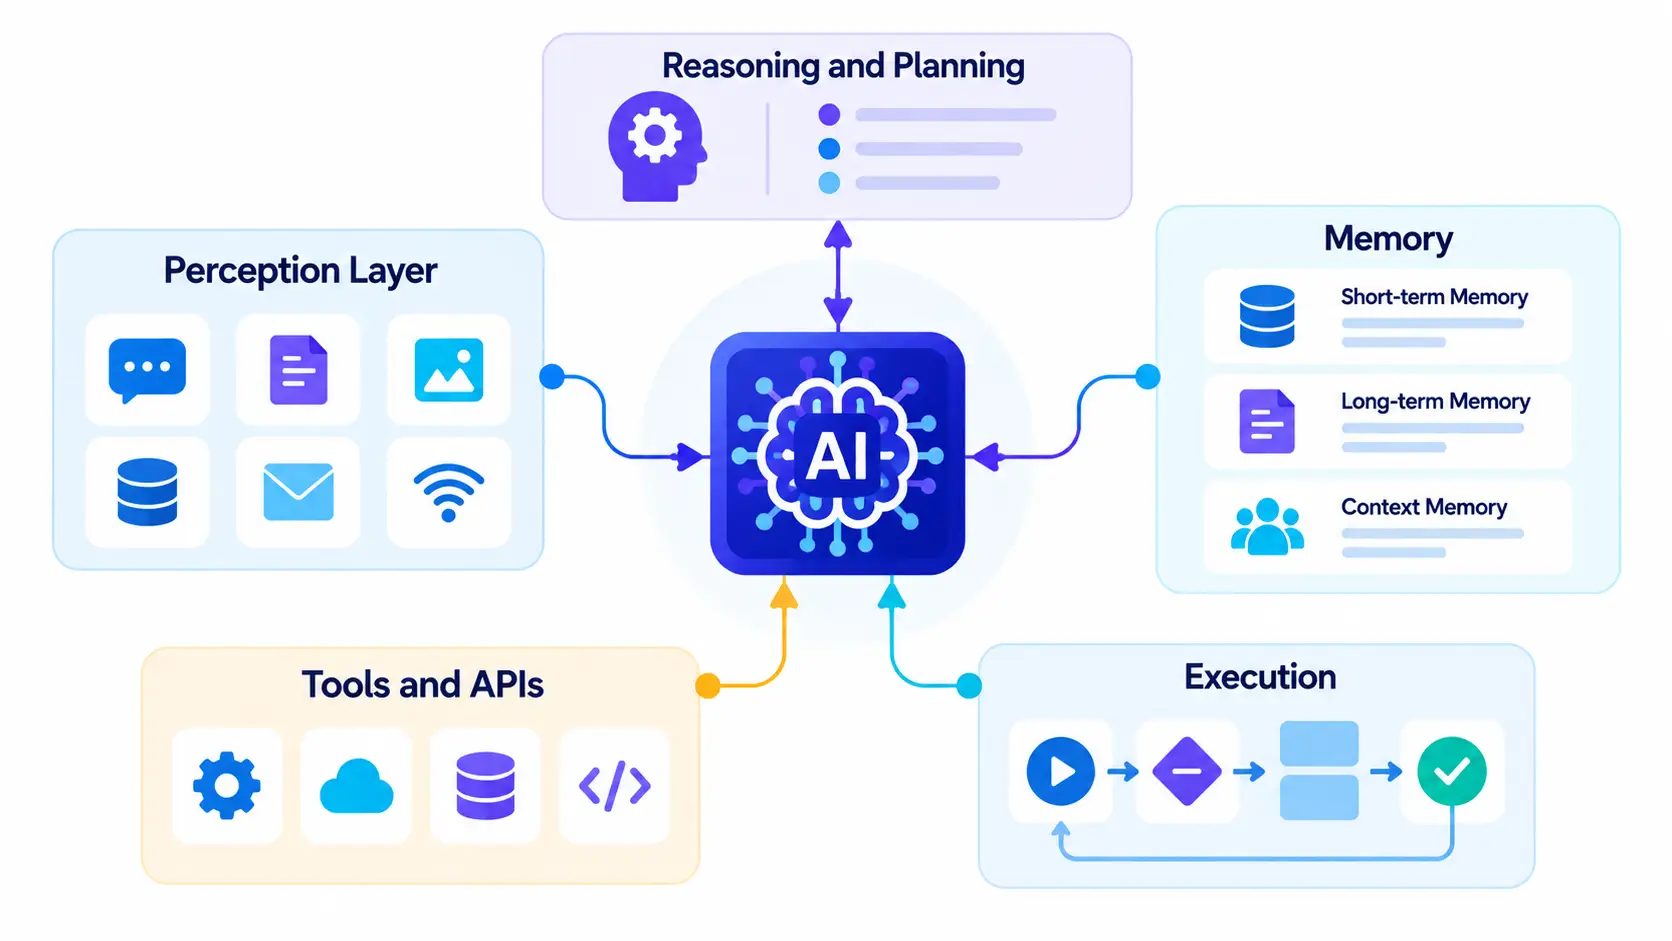
- Perception layer: How the agent receives information, whether that is a user message, a system event, a document, or an API trigger. This is the agent’s view of its environment.
- Reasoning and planning engine: Almost always a large language model. This is the component that interprets the goal, breaks it into steps, and decides what to do next.
- Memory: Short-term memory for the current task and long-term memory for context across sessions. Agents handling multi-turn workflows typically need both, often backed by a vector database for retrieval.
- Tool and API integration: The layer that separates an agent from a chatbot. This is what lets it query a CRM, update a database, or trigger a workflow in another system.
- Action and execution layer: The component that actually performs the decided action, whether that is sending an email, writing a record, or escalating to a human reviewer.
Getting the LLM connected to real tools is usually the first serious technical hurdle in a build. Teams that have gone through implementing AI into an app using OpenAI’s APIs know this is where a proof of concept either turns into something production-ready or stays a demo.
Single-Agent or Multi-Agent: How to Decide
A single agent operates independently, using external tools to complete a well-defined task. This is the right starting point for most projects: it is cheaper to build, easier to test, and far easier to debug when something goes wrong.

A multi-agent system splits the work across multiple specialized agents that collaborate or hand off tasks, coordinated by an orchestration layer. This adds real engineering weight (coordination logic, shared memory, conflict resolution), so it should only enter the conversation when a task genuinely spans domains a single agent cannot reasonably handle. A hierarchical customer operations system, where one agent triages a request and routes it to specialized billing, technical, or account-management agents, is a legitimate case. A single support agent that just looks up an order and issues a refund is not.
| Editor’s note: The most common architecture mistake we see is teams reaching for a multi-agent system because it sounds more sophisticated, when the actual workflow is a single, well-bounded task. Multi-agent orchestration triples the testing surface and the failure modes. Reserve it for genuinely cross-domain work. |
Different types of agent and their best fit
Here is how the main types map to real business scenarios.
| Agent type | How it decides | Best fit |
| Simple reflex | Fixed condition-action rules | High-volume, repetitive tasks with no ambiguity (routing tickets by keyword) |
| Model-based | Rules plus a limited internal state | Personalization based on recent history (recommend based on last few actions) |
| Goal-based | Plans a sequence of steps toward an objective | Multi-step workflows with a clear end state (reroute a delivery, resolve a ticket) |
| Utility-based | Weighs multiple outcomes and picks the highest-value one | Decisions with real trade-offs (fraud scoring, trading logic) |
| Learning | Improves through feedback over time | Personalization engines, recommendation systems |
| Multi-agent | Specialized agents coordinating on a shared goal | Enterprise workflow orchestration across departments |
Also Read: What is React Native and Why Choose it for AI-Powered Business Apps?
Where AI Agents Deliver Value Across Industries
AI agents are already doing production work across most major verticals, and the specifics of what they automate tend to follow the shape of each industry’s operational bottlenecks.
- Customer support: Agents triage and resolve Tier 1 tickets, process returns, and escalate complex cases with full context attached, cutting average handling time without adding headcount.
- Financial services: Invoice reconciliation, anomaly flagging, and compliance-check automation are common starting points, since these tasks are high-volume, rules-heavy, and easy to measure. Teams building consumer-facing money tools are seeing similar gains; our guide to AI-powered personal finance app development covers how agents shift these apps from static trackers into proactive assistants.
- Healthcare: Appointment scheduling, patient intake, and prior-authorization workflows are prime candidates because they are repetitive, time-consuming, and don’t require clinical judgment.
- E-commerce: Personalized product recommendations, inventory monitoring, and order-management automation are where agents show up first, since the data needed to power them already exists in most commerce platforms.
- Real estate: Lead qualification, showing coordination, and document routing between agents, buyers, and sellers are increasingly agent-driven tasks.
- IT operations: Automatic triage and resolution of routine incidents, with escalation to human engineers only when the agent hits the edge of its playbook.
The common thread across all of these is volume plus repeatability: tasks that happen often, follow a describable process, and have a measurable outcome are the strongest early candidates, regardless of industry.
Build vs Buy: Choosing Your AI Agent Development Path

There are three real paths into AI agent development, and most teams end up in the third one even if they start out thinking in binary terms.
- Building from scratch gives you full control over data handling, decision logic, and how the agent integrates with your existing systems. It takes longer and requires in-house or contracted engineering depth, but for a highly specific workflow tied to proprietary business logic, that investment pays off.
- Buying a pre-built platform gets you to a working agent faster, especially for common use cases like customer support or basic lead qualification. The tradeoff is flexibility: pre-built platforms are optimized for the common case, and edge cases specific to your business often require workarounds that erode the time savings.
- A hybrid approach, using an established framework for orchestration and model access while building custom integration and business logic on top, is what most production deployments actually look like in 2026. This gets you proven infrastructure for the genuinely commoditized parts (LLM access, basic orchestration) while keeping control over the parts that actually differentiate the product (how it connects to your systems, what decisions it is allowed to make).
The decision usually comes down to one question: is the workflow generic enough that a competitor on the same off-the-shelf platform would end up with roughly the same agent? If yes, buy. If the value lies in how the agent handles your specific data and edge cases, build or go hybrid.
What Does AI Agent Development Cost in 2026?
Cost is where most of the ambiguity in agent projects lives, and it is also where scoping mistakes get expensive fast. The single biggest driver is not the model you choose. It is integration depth: how many systems the agent needs to read from and write to, and how legacy or well-documented those systems are.
| Complexity tier | Typical scope | Estimated cost range | Timeline |
| Simple agent | Single task, one or two integrations, no persistent memory | $8,000 – $40,000 | 4–8 weeks |
| Mid-complexity agent | Multi-step workflow, retrieval-augmented memory, several integrations | $40,000 – $150,000 | 3–5 months |
| Enterprise multi-agent system | Cross-department orchestration, compliance requirements, high-volume interactions | $150,000 – $450,000+ | 6–12 months |
Ongoing costs deserve just as much attention as the build. Maintenance, including model updates, retraining, and security patching, typically runs 15 to 30 percent of the original development cost annually. Compliance-heavy industries add another layer: HIPAA, SOC 2, or audit-grade logging requirements commonly add a 15 to 30 percent premium to the build, since encryption, role-based access, and immutable audit trails are cheaper to design in early than to retrofit later.
| Editor’s note: The costs that surprise first-time buyers rarely show up in the initial quote. Data cleanup, evaluation and safety testing, and change management for the staff who will work alongside the agent routinely add 20 to 30 percent to a project’s total cost. Ask any development partner to itemize these explicitly before signing off on a budget. |
Token and inference costs also compound at scale in ways that are easy to underestimate during a proof of concept. A workflow costing a few dollars per thousand interactions in testing can look very different once volume climbs into the tens of thousands monthly, especially for agents with long context windows or heavy tool-calling depth. Budgeting for operating costs, not just the build fee, is one of the clearest signals of a well-scoped project.
Step-by-Step: How to Build a Production-Ready AI Agent
A production-ready agent generally moves through five stages, and skipping any of them is where most of the “it worked in the demo” failures come from.
- Define the use case and success criteria. The strongest candidates are high-volume, repeatable tasks with a measurable outcome. Vague goals like “improve customer service” do not translate into a buildable scope; “resolve password reset tickets without human intervention” does.
- Choose the architecture and framework. Decide on single-agent versus multi-agent, select the underlying model based on latency, context window, and cost requirements, and settle on a memory strategy before writing any integration code.
- Select tools, data sources, and integrations. Map out exactly which systems the agent needs read and write access to, and just as importantly, define what actions require human approval versus what the agent can do autonomously.
- Build, test, and evaluate. This stage consumes the most time in any well-run project. Prompt engineering, tool-calling logic, and structured testing against edge cases matter more here than model selection, since an agent that performs well in a demo can behave unpredictably once it meets real, messy production data.
- Deploy, monitor, and scale. Launch with observability in place from day one, not added after something breaks. Track task success rate, escalation frequency, and cost per interaction, and build a feedback loop so the agent’s performance data actually informs the next iteration.
Teams that treat step four as a formality rather than the core of the project end up back at step one a few months later.
Also Read: How AI is Changing the E-commerce Industry?
Common AI Agent Pitfalls and How to Fix Them?

Challenge: Hallucination and wrong actions. Agents given too much autonomy without guardrails can take incorrect actions with real consequences, not just generate a wrong answer in a chat window.
Fix: Scope agent autonomy tightly at launch. Require human approval for any action that is difficult to reverse (payments, account changes, external communications) and expand autonomy only after the agent has demonstrated reliable performance on lower-stakes actions.
_________________________________________________________________________________________
Challenge: Integration complexity with legacy systems. Older platforms without modern APIs turn what looked like a straightforward integration into a multi-week middleware project.
Fix: Audit system access and data quality before finalizing scope or budget, not after development starts. A middleware layer that standardizes communication with legacy systems is often cheaper in the long run than repeated one-off workarounds.
_________________________________________________________________________________________
Challenge: LLM and infrastructure costs can escalate at scale. Costs that looked reasonable in testing can become a real constraint once usage climbs, especially for agents with deep tool-calling chains.
Fix: Use smaller, cheaper models for routine sub-tasks and reserve larger models for steps that require complex reasoning. This tiered model approach commonly cuts production costs by 40 to 60 percent with no noticeable drop in quality.
_________________________________________________________________________________________
Challenge: Governance gaps and unclear accountability. When an agent makes a wrong call, unclear ownership over who is accountable and no audit trail to review turns a fixable mistake into a trust problem.
Fix: Build logging and audit trails from the start, assign a clear internal owner for each production agent, and define escalation paths before launch, not after the first incident.
_________________________________________________________________________________________
Challenge: Security exposure through tool access. Every tool an agent can call is a potential attack surface, and prompt injection remains one of the most common ways agents are manipulated into taking unintended actions.
Fix: Apply the principle of least privilege to every tool integration, log every tool call, and treat any user-supplied content that reaches the agent’s context window as untrusted input requiring validation.
How Do You Know Your AI Agent Is Working?
Shipping an agent is not the finish line. Teams that get real value from AI agent development define what “working” means before launch, then track it consistently afterward.
- Task success rate: The percentage of interactions the agent completes correctly without human intervention. This is the single clearest signal of whether the agent is production-ready or still needs tuning.
- Escalation rate: How often the agent hands off to a human, and why. A high escalation rate on a specific task type usually points to a gap in the agent’s tools or training data, not a fundamental flaw in the approach.
- Cost per interaction: Track this from day one so cost creep is visible early rather than discovered in a quarterly budget review.
- Containment rate: For support-style agents specifically, the share of interactions the agent resolves without ever looping in a human is often the metric that most directly maps to ROI.
Ongoing maintenance and monitoring are what keep these numbers from drifting once real users start interacting with the system. Our breakdown of how AI is transforming app maintenance and support covers the monitoring practices that apply directly to agents running in production, not just traditional software.
Final Thoughts
The organizations pulling ahead with AI agents in 2026 are not the ones with the most sophisticated architecture. They are the ones who scoped the right problem, built in governance from day one, and measured what mattered after launch instead of treating deployment as the finish line. Agentic AI is still moving fast enough that the frameworks and models available today will look different in eighteen months, but the underlying discipline- defining a clear task, choosing the right level of autonomy, and building in oversight from the start- does not change with the tooling.
If you’re scoping an AI agent project and want a clearer picture of what it would actually take to build, Simpalm’s agentic AI development team can walk through your specific use case and help you figure out where the real complexity and cost live before you commit to a timeline.
Frequently Asked Questions
Q1. What is the difference between an AI agent and generative AI?
Generative AI refers to models that produce new content, text, images, or code, in response to a prompt. An AI agent uses generative AI (typically an LLM) as its reasoning engine, but adds planning, memory, and the ability to call tools and take actions. In short, generative AI produces output, while an AI agent uses that output to actually do something in a system.
Q2. How long does it take to build an AI agent?
A simple, narrowly scoped agent can go from kickoff to production in four to eight weeks. Mid-complexity agents with retrieval-augmented memory and several integrations typically take three to five months. Full multi-agent enterprise systems with compliance requirements often run six to twelve months, and these timelines assume a team with prior agent-delivery experience rather than one learning the architecture from scratch mid-project.
Q3. Do I need a large language model for every AI agent?
No, if the task involves clear, structured decisions with no real ambiguity, a rules-based or model-based agent will be cheaper to build, easier to audit, and more predictable than an LLM-powered one. LLMs earn their cost on tasks involving unstructured input or a large number of possible paths through a workflow, not on tasks that could be handled with a decision tree.
Q4. How much ongoing maintenance does an AI agent need after launch?
Plan for 15 to 30 percent of the original development cost annually, covering model updates, retraining, security patching, and continuous evaluation against real failure cases. Agents that launch without a defined maintenance owner tend to perform well for the first few months, then quietly degrade as the business processes around them change.
Q5. What industries see the fastest return on AI agent investment?
Customer support, finance, and IT operations tend to show the clearest early ROI, largely because these functions already have high transaction volume, well-documented processes, and existing systems with APIs the agent can connect to. Industries with heavier compliance requirements, like healthcare and financial services, can still see strong returns, but the build typically takes longer because governance and audit requirements need to be designed in from the start.
Q6. How do I choose between building an AI agent in-house and hiring a development partner?
The right choice depends less on budget and more on whether your team has already shipped agent-based systems into production. In-house development makes sense when AI is core to your product, and you have engineers with relevant experience. A development partner is usually faster and lower-risk for a first agent project, since an experienced team will already have solved the integration and governance issues that tend to blow up timelines for first-time builders.